Case Study 18 — Security Onion Deployment & Network Security Monitoring
Security Onion Deployment & Network Security Monitoring
UI Operations deployed a distributed Security Onion platform to deliver continuous network monitoring, intrusion detection, centralized logging, and real-time security alerting—helping an enterprise security team identify, investigate, and respond to threats across its infrastructure.
Security Onion
Suricata
Zeek
Elastic Stack
Intrusion Detection
Project at a Glance
Client
Confidential Enterprise Client
Project
Security Onion Deployment & Network Security Monitoring
Service
Security Monitoring & Infrastructure Deployment
Platform
Security Onion
Core Technologies
Suricata, Zeek, Elasticsearch, Logstash, Kibana
Focus
Intrusion Detection, Network Traffic Analysis, Centralized Logging, Incident Response & Scalability
UI Operations implemented a distributed Security Onion deployment to strengthen the client’s network security monitoring capabilities.
The solution integrated Suricata intrusion detection, Zeek network traffic analysis, and the Elastic Stack for centralized log collection, correlation, and visualization. Real-time alerts, packet capture, role-based access controls, and redundant infrastructure supported incident investigation and continuous monitoring.
The result was a scalable security monitoring environment designed to provide greater visibility across the client’s network and support faster, more informed security operations.
The Challenge
Gaining Complete Visibility Across a Complex Enterprise Network.
The client needed a unified solution capable of monitoring diverse network traffic, identifying suspicious activity, and managing growing volumes of security data without overwhelming its security team.
Detecting Network Threats
The client required signature-based and anomaly-based intrusion detection across complex network traffic and protocols.
Fragmented Security Data
Logs from firewalls, servers, routers, and network sensors needed to be centralized for effective investigation and analysis.
Alert Volume & Scalability
The monitoring environment needed to reduce alert fatigue, handle increasing log volumes, and remain available as the network expanded.
The Solution
An Integrated Security Monitoring Platform Built for Enterprise Visibility.
UI Operations deployed Security Onion in a distributed configuration, combining network sensors, traffic analysis, centralized logging, and incident investigation capabilities.
Intrusion Detection & Traffic Analysis
Deployed Suricata and Zeek to identify suspicious network activity, analyze protocols, and generate detailed security events.
Centralized Logging & Analytics
Configured Elasticsearch, Logstash, and Kibana to collect, normalize, search, correlate, and visualize security data.
Incident Investigation & Alerting
Enabled event correlation, real-time notifications, and packet capture to support security investigations and response.
Distributed & Resilient Architecture
Deployed distributed components with Elasticsearch data replication, horizontal scaling capabilities, and secure role-based access.
Architecture & Technology
Inside the Security Onion Monitoring Architecture.
The deployment used distributed Security Onion components to collect and analyze network traffic and security logs. Suricata generated intrusion alerts, Zeek provided protocol and connection analysis, and the Elastic Stack centralized data processing, storage, and visualization.
Unified Visibility Across Security Events
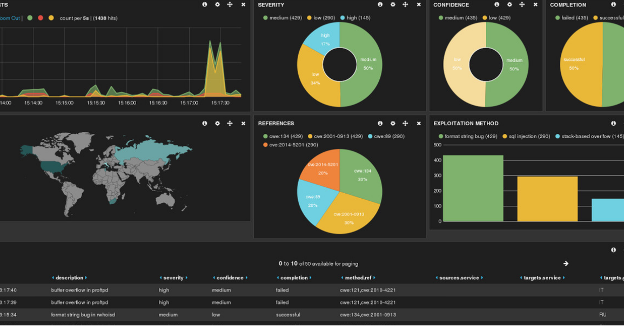
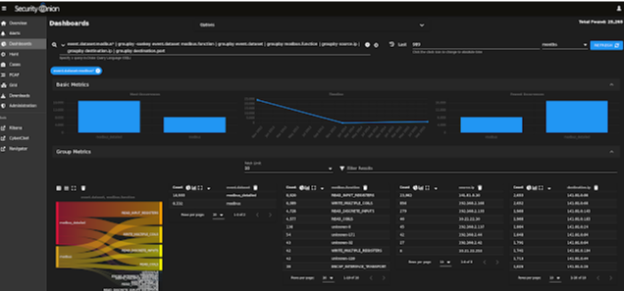
Security analytics dashboard illustrating event trends, geographic activity, alert categories, and network security data used to support centralized monitoring.
Turning Network Logs Into Actionable Security Insights
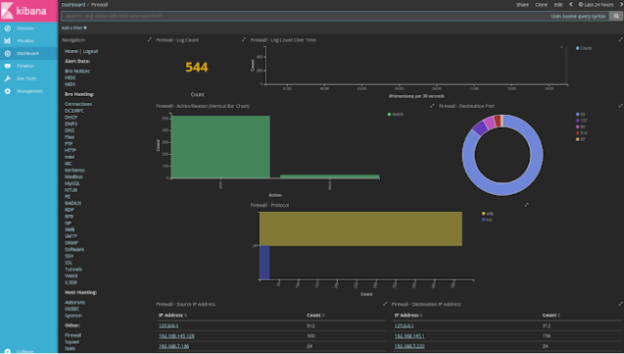
Kibana dashboard displaying security event statistics, visualizations, and log analysis to support threat investigation and monitoring.
Our Implementation Approach
Plan
Assessed network scale, traffic volume, sensor placement, and infrastructure resource requirements.
Deploy
Installed Security Onion using a distributed deployment architecture with appropriately sized components.
Detect
Configured Suricata intrusion detection and Zeek protocol analysis across network sensors.
Centralize
Integrated Elasticsearch, Logstash, and Kibana for log processing, storage, dashboards, and search.
Respond
Configured event correlation, critical alerts, email and Slack notifications, and packet-based investigation capabilities.
Harden & Scale
Implemented data replication, role-based access controls, TLS communications, and horizontal scaling provisions.
Technical Challenges & Solutions
Overcoming Complex Security Monitoring Challenges.
Complex Network Traffic
Challenge: The client's infrastructure included diverse protocols and communication patterns, complicating traffic analysis. Solution: Fine-tuned Suricata and Zeek configurations to improve visibility and detection across the network.
High Security Data Volumes
Challenge: Large volumes of logs and metrics created performance and storage-management demands. Solution: Optimized Elasticsearch indices and data retention policies to support efficient log storage and analysis.
Alert Fatigue
Challenge: Excessive false positives and repetitive notifications could overwhelm security analysts. Solution: Tuned alert thresholds and implemented event correlation to prioritize meaningful security alerts.
Monitoring, Optimization & Handover
Real-Time Detection. Centralized Intelligence. Faster Investigation.
Continuous Network Visibility
Suricata and Zeek analyze network activity, producing intrusion alerts, protocol logs, and security event data.
Real-Time Security Alerting
Correlated alerts and notifications through email and Slack help security teams identify critical events promptly.
Packet Capture & Forensics
Full packet capture supports detailed traffic investigation, incident analysis, and examination of suspicious activity.
Secure & Resilient Operations
Role-based access, TLS encryption, replicated Elasticsearch data, and distributed sensors support secure monitoring operations.
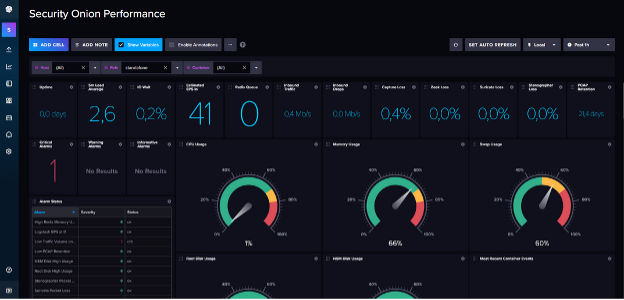
Tracking Security Events & Activity Patterns
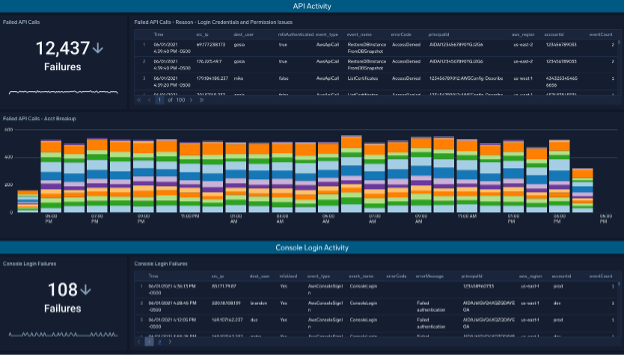
Security monitoring dashboard displaying activity trends and event records to support historical analysis and operational review.
Results & Business Impact
Greater Visibility. Stronger Detection. Scalable Security Operations.
Comprehensive Intrusion Detection
Established continuous intrusion detection and traffic analysis through Suricata and Zeek.
Centralized Security Intelligence
Consolidated network and device logs into a searchable environment for analysis and investigation.
Real-Time Security Alerts
Enabled critical-event notifications and correlated alerts to support timely investigation and response.
Scalable & Resilient Monitoring
Implemented distributed components, replicated data, and an architecture designed for future network growth.
Business Impact Summary
The Security Onion deployment gave the client a centralized and scalable security monitoring environment, combining intrusion detection, network traffic analysis, log management, alerting, and incident investigation. By reducing fragmented visibility and improving security event correlation, the solution strengthened the security team's ability to identify suspicious activity and respond to potential threats.
Tools & Technology Used
Security Onion
Suricata
Zeek
Elasticsearch
Logstash
Kibana
Elastic Stack
Full Packet Capture
Role-Based Access
SSL/TLS
Ansible
Distributed Sensors
Security Onion
Suricata
Zeek
Elasticsearch
Logstash
Kibana
Elastic Stack
Full Packet Capture
Role-Based Access
SSL/TLS
Ansible
Distributed Sensors
Conclusion
Building a More Visible, Resilient & Proactive Security Environment.
The Security Onion Deployment project delivered an integrated monitoring solution designed to detect network threats, centralize security data, and support timely incident investigation.
Through distributed deployment, intrusion detection, traffic analysis, alert correlation, and resilient logging infrastructure, UI Operations established a scalable foundation for continuous security monitoring and future operational growth.
RELATED CASE STUDIES
Explore More Case Studies
LET’S BUILD WHAT’S NEXT
Ready to Gain Complete Visibility Into Your Network Security?
From intrusion detection and network traffic analysis to centralized logging and security monitoring, UI Operations helps organizations strengthen their security operations with scalable, integrated solutions.