Case Study 19 — Wazuh Deployment & Security Monitoring Integration
Wazuh Deployment & Enterprise Security Monitoring
UI Operations deployed Wazuh across a financial services organization’s infrastructure, delivering centralized security monitoring, real-time threat detection, log analysis, and compliance reporting through a scalable, cost-effective security platform.
Wazuh
Threat Detection
SIEM Integration
Compliance Monitoring
Project at a Glance
Client
Mid-Sized Financial Services Company — Confidential
Project
Wazuh Deployment & Enterprise Security Monitoring
Service
Security Monitoring & SIEM Integration
Platform
Wazuh
Deployment
Centralized Wazuh Manager & Distributed Agents
Focus
Threat Detection, Log Analysis, Compliance, Scalability & Cost Efficiency
UI Operations implemented Wazuh, an open-source security monitoring platform, to strengthen the client’s infrastructure visibility and threat detection capabilities.
The deployment included a dedicated Wazuh Manager, distributed monitoring agents, centralized log aggregation, SIEM integration, customized security rules, and automated compliance reporting aligned with PCI-DSS, GDPR, and SOX requirements.
The resulting solution provided a scalable security monitoring foundation while reducing reliance on costly proprietary tools.
The Challenge
Strengthening Security Visibility Across a Regulated Enterprise.
The client required a centralized, cost-effective security monitoring solution capable of identifying threats in real time, managing logs from multiple infrastructure sources, and supporting regulatory compliance as the organization continued to grow.
Limited Threat Visibility
Security events across endpoints, servers, and network systems needed centralized monitoring and real-time detection.
Complex Compliance Requirements
The organization needed audit trails and reporting capabilities to support PCI-DSS, GDPR, and SOX obligations.
Fragmented Logs & Rising Costs
Disparate security logs and budget constraints required an integrated, scalable alternative to proprietary monitoring solutions.
The Solution
Centralized Threat Detection, Log Intelligence & Compliance Monitoring.
UI Operations deployed Wazuh to unify security event monitoring across the client’s infrastructure, integrating endpoint telemetry, log analysis, automated alerts, and compliance reporting within one operational framework.
Real-Time Security Monitoring
Deployed Wazuh agents and customized detection rules to identify malware, unauthorized access, and suspicious activity.
Centralized Log Management
Aggregated system, application, firewall, and IDS logs through Wazuh and the existing SIEM environment.
Automated Compliance Reporting
Configured compliance rules and audit reporting to support PCI-DSS, GDPR, and SOX requirements.
Scalable & Resilient Deployment
Optimized manager and agent configurations and implemented load balancing and failover for high availability.
Architecture & Technology
Inside the Wazuh Security Monitoring Architecture.
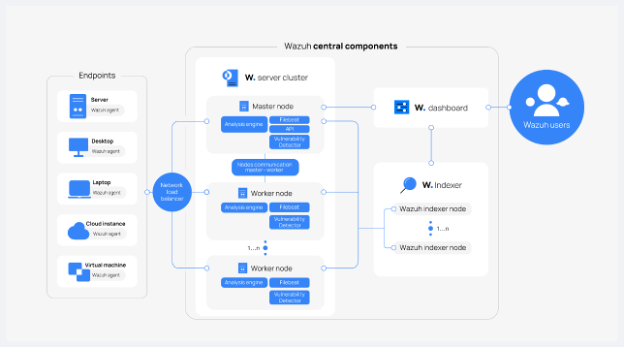
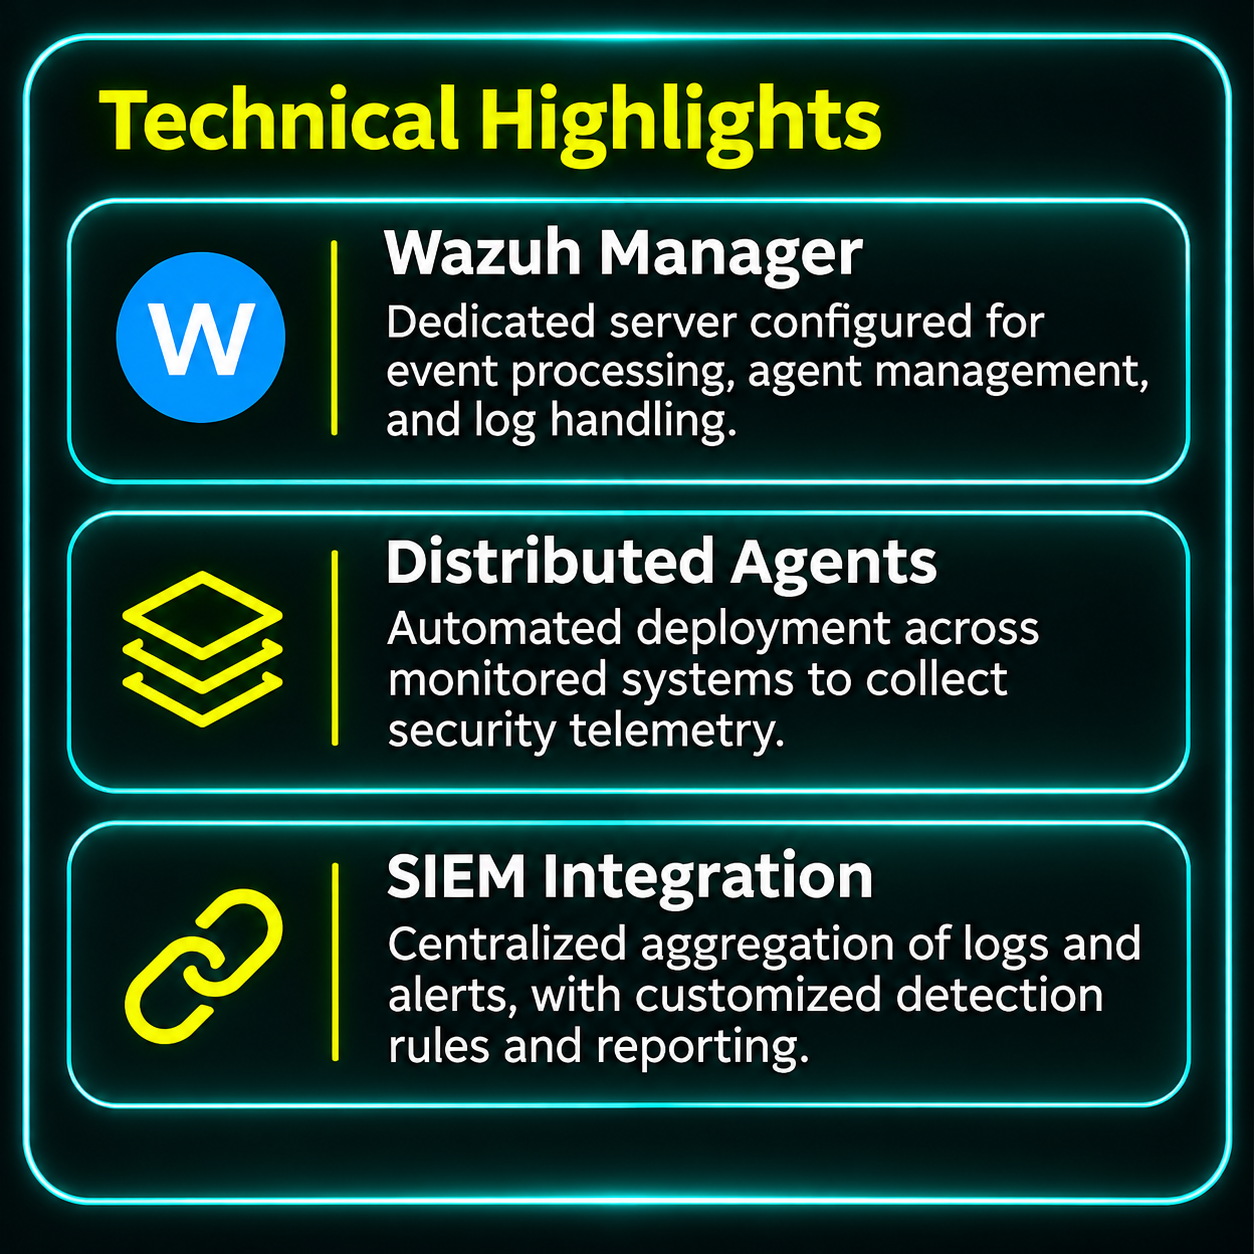
The solution used a centralized Wazuh Manager deployed on a dedicated server, with monitoring agents installed across the client’s infrastructure.
Security events and logs were collected from endpoints, servers, firewalls, databases, and intrusion detection systems, then processed through Wazuh and integrated with the client’s SIEM platform for centralized analysis.
Centralized Security Monitoring Across Enterprise Infrastructure
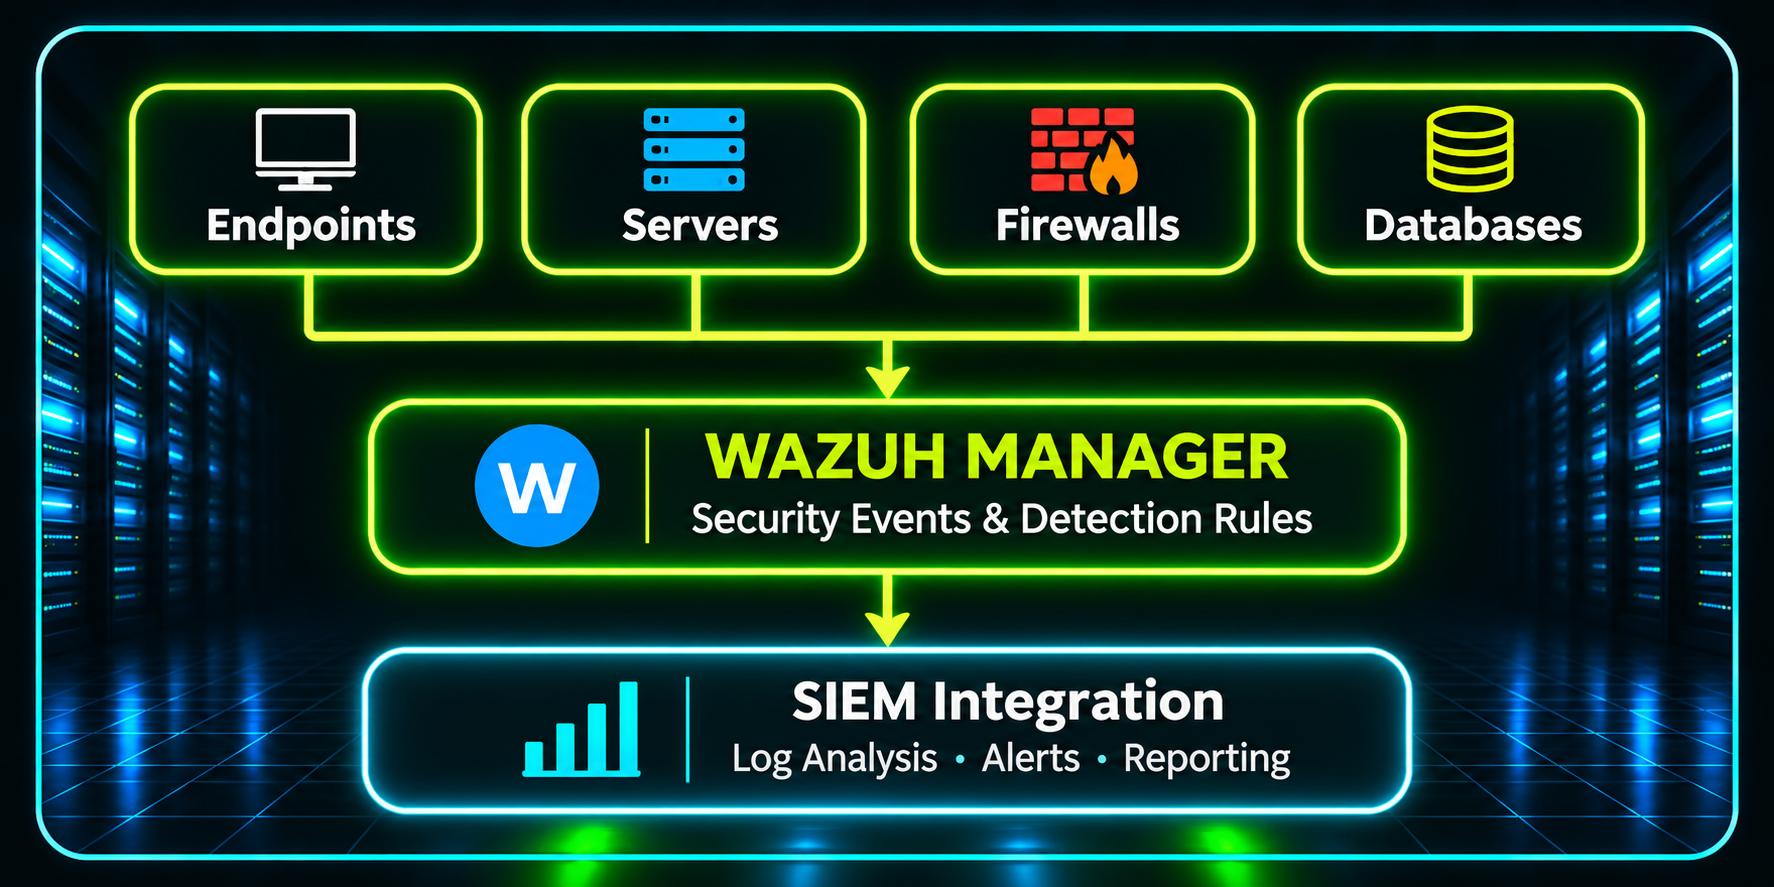
Conceptual architecture illustrating how Wazuh collects and processes security events from distributed infrastructure sources and integrates with a SIEM platform for analysis and reporting.
Our Implementation Approach
Assess & Plan
Reviewed infrastructure, security tools, monitoring requirements, and deployment constraints.
Deploy
Configured the Wazuh Manager and deployed agents using automated installation scripts.
Integrate
Connected system, application, firewall, and IDS logs with the existing SIEM environment.
Configure
Customized detection rules, alert thresholds, compliance reporting, and audit controls.
Validate & Optimize
Tested simulated incidents, SIEM data flow, system performance, load balancing, and failover.
Handover & Support
Delivered administrator training, documentation, operational handover, and ongoing support planning.
Technical Challenges & Solutions
Overcoming Complex Security Monitoring Challenges.
Integration With Existing Security Systems
Challenge: Connecting Wazuh with the client's existing SIEM and security tools required careful configuration and validation. Solution: Coordinated with the client's IT team to configure integrations and test reliable security event data flow.
High-Volume Log Processing
Challenge: Large volumes of logs from distributed infrastructure placed demands on event processing and system performance. Solution: Tuned Wazuh Manager resources, agent configurations, logging frequency, and event processing parameters.
Operational Knowledge Transfer
Challenge: The client's internal security team needed the skills and documentation to independently manage the platform. Solution: Conducted hands-on training and delivered comprehensive operational documentation, configuration guidance, and a support plan.
Monitoring, Optimization & Handover
Continuous Detection. Centralized Intelligence. Audit-Ready Reporting.
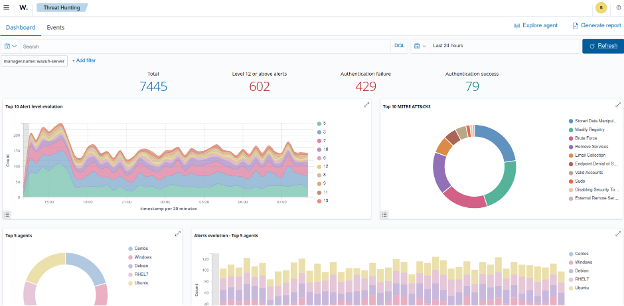
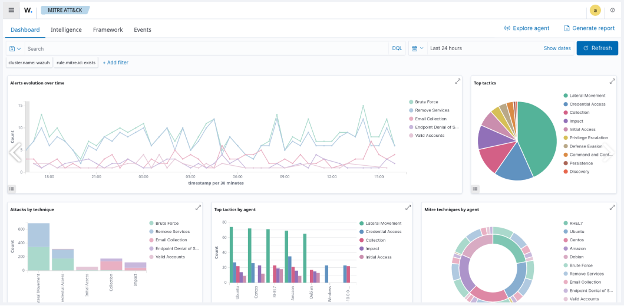
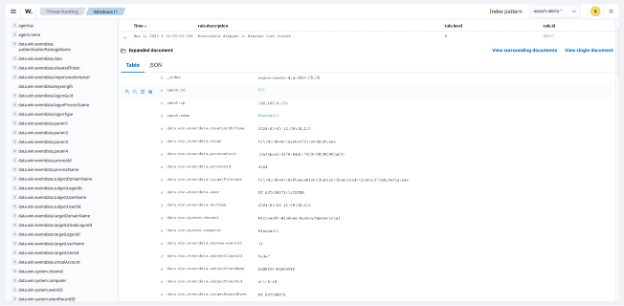
Real-Time Threat Detection
Customized Wazuh rules detect malware, unauthorized access attempts, and network intrusion activity.
Centralized Log Analysis
Security logs from endpoints, servers, firewalls, applications, and intrusion detection systems are consolidated for analysis.
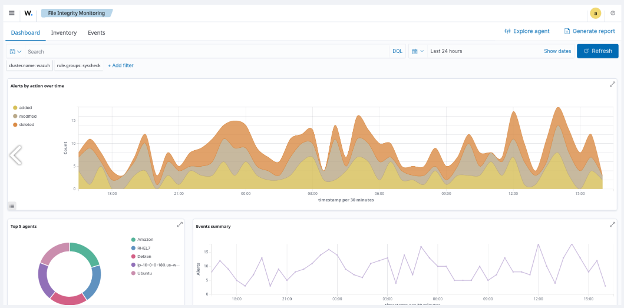
Compliance Reporting & Audit Trails
Automated reports and custom compliance rules support security control reviews against PCI-DSS, GDPR, and SOX requirements.
Security Alert Tuning
Customized thresholds and detection sensitivities help reduce false positives and prioritize meaningful security alerts.
Results & Business Impact
Greater Visibility. Stronger Compliance Support. Lower Monitoring Cost
Enhanced Security Visibility
Enabled centralized monitoring and real-time detection across critical infrastructure systems.
Improved Compliance Support
Established automated reporting and audit trails to assist with PCI-DSS, GDPR, and SOX requirements.
Centralized Log Intelligence
Consolidated logs from multiple infrastructure sources to streamline analysis and security investigations.
Cost-Effective Scalability
Delivered an open-source monitoring platform designed to expand with infrastructure growth while reducing proprietary tooling costs.
Business Impact Summary
The Wazuh deployment strengthened the client's security monitoring capabilities by consolidating infrastructure logs, enabling real-time detection, and simplifying compliance reporting. Its open-source architecture provided a scalable, cost-conscious foundation for ongoing security operations, while training and operational handover enabled the client's internal team to manage the platform effectively.
Tools & Technology Used
Wazuh
Wazuh Manager
Wazuh Agents
SIEM Integration
Elastic Stack
Log Analysis
Intrusion Detection
Compliance Reporting
PCI-DSS
GDPR
SOX
Load Balancing & Failover
Wazuh
Wazuh Manager
Wazuh Agents
SIEM Integration
Elastic Stack
Log Analysis
Intrusion Detection
Compliance Reporting
PCI-DSS
GDPR
SOX
Load Balancing & Failover
Conclusion
Building a More Secure, Visible & Compliant Infrastructure.
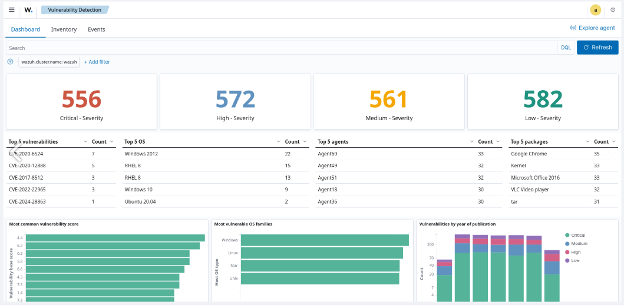
The Wazuh Deployment project delivered an integrated security monitoring solution tailored to the operational and regulatory requirements of a financial services organization.
By combining centralized log management, customized threat detection, compliance reporting, and resilient deployment architecture, UI Operations established a scalable platform for continuous security monitoring and future infrastructure growth.
RELATED CASE STUDIES
Explore More Case Studies
LET’S BUILD WHAT’S NEXT
Ready to Strengthen Your Security Monitoring & Compliance?
From Wazuh deployment and SIEM integration to centralized logging, threat detection, and compliance monitoring, UI Operations helps organizations gain better visibility and control over their security infrastructure.