CASE STUDY 06 / ENDPOINT SECURITY & THREAT DETECTION
Cortex XDR Deployment & Integration
UI Operations deployed and integrated Palo Alto Networks Cortex XDR to strengthen enterprise endpoint protection, centralize security monitoring, and accelerate incident response across the client’s existing IT and cloud environments.
Cortex XDR
Endpoint Security
Threat Detection
SIEM Integration
Incident Response
Project at a Glance
Client
Confidential Enterprise Client
Project
Cortex XDR Deployment & Integration
Service
Security Consulting & Integration
Platform
Palo Alto Networks Cortex XDR
Solution
Endpoint Detection & Response (EDR) Deployment
Focus
Threat Detection, SIEM Integration, Automation & Cloud Security
Deployed and integrated Cortex XDR across enterprise endpoints and cloud environments, connecting it with existing security tools and SIEM systems to improve threat visibility, automate incident response, and strengthen overall cybersecurity resilience.
The Challenge
Strengthening Threat Detection Across a Complex Enterprise Environment.
The client required a unified cybersecurity solution capable of protecting a growing network of endpoints and cloud workloads while integrating with existing security infrastructure.
The solution needed to deliver advanced threat detection, centralized visibility, automated response, and scalability without disrupting existing operations.
Advanced Threat Protection
Detect sophisticated attacks across endpoints and cloud environments using behavioral analytics and machine learning.
Fragmented Security Visibility
Unify endpoint security monitoring, alerts, and reporting with existing SIEM and security tools.
Incident Response & Scale
Accelerate threat containment while supporting a growing enterprise device and cloud environment.
The Solution
A Unified Platform for Detection, Response, and Security Visibility.
UI Operations deployed Cortex XDR across the client’s endpoint infrastructure and integrated the platform with existing SIEM, firewall, anti-malware, and threat intelligence systems.
The implementation combined centralized monitoring, advanced analytics, cloud workload visibility, and automated response capabilities to strengthen enterprise-wide security operations.
Enterprise Endpoint Protection
Deployed Cortex XDR agents across laptops, desktops, and mobile endpoints for advanced detection and response.
SIEM & Security Integration
Integrated Cortex XDR with existing SIEM and firewall infrastructure for centralized event visibility and threat intelligence sharing.
Advanced Threat Detection
Enabled machine learning, behavioral analytics, and external threat intelligence to improve detection of emerging threats.
Automated Incident Response
Configured response capabilities to support rapid containment, remediation, and reduced operational disruption.
Architecture & Technology
Inside the Cortex XDR Security Integration.
The deployment connected enterprise endpoints, cloud workloads, and existing security infrastructure through Cortex XDR, enabling centralized threat detection, monitoring, and coordinated response.
integration architecture based on the deployment
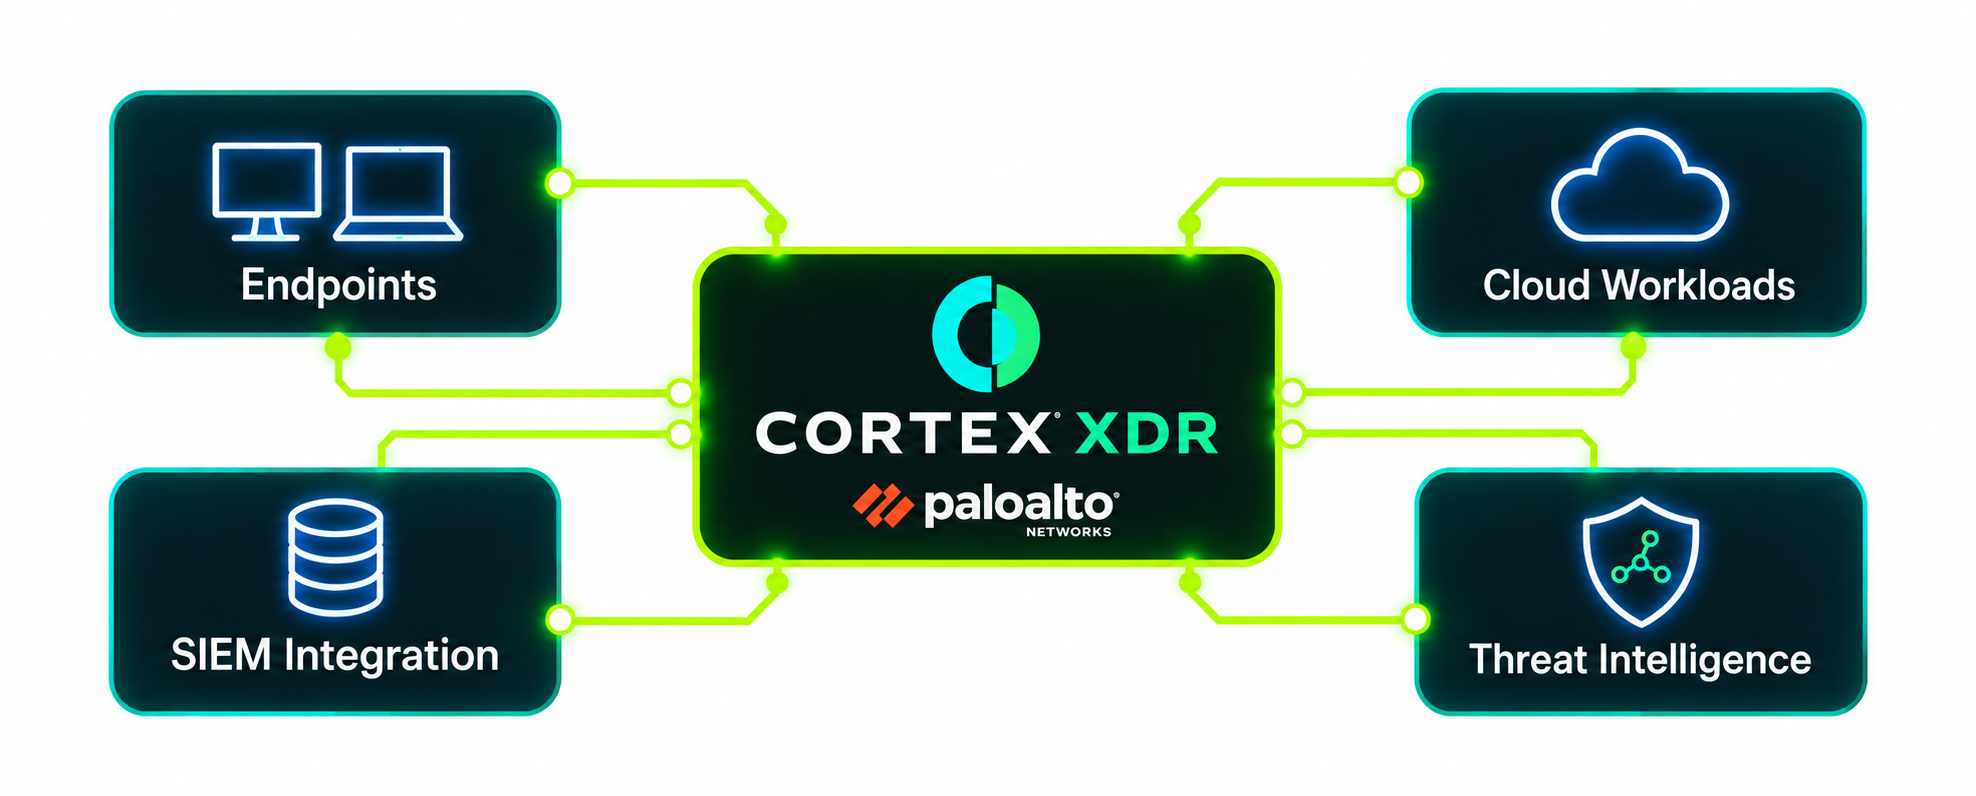
Illustrative simplified topology
Centralized Security Monitoring
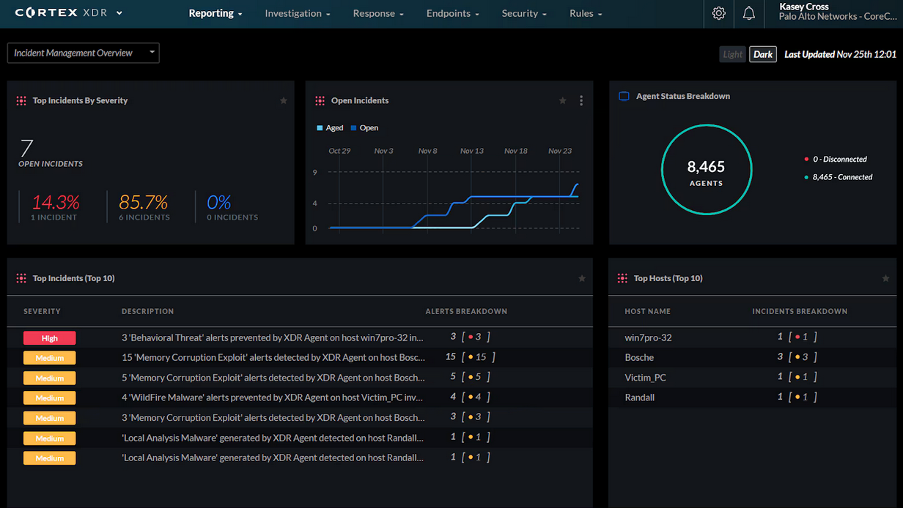
A unified dashboard for incident tracking, alert monitoring, and security analytics.
Incident Investigation & Response
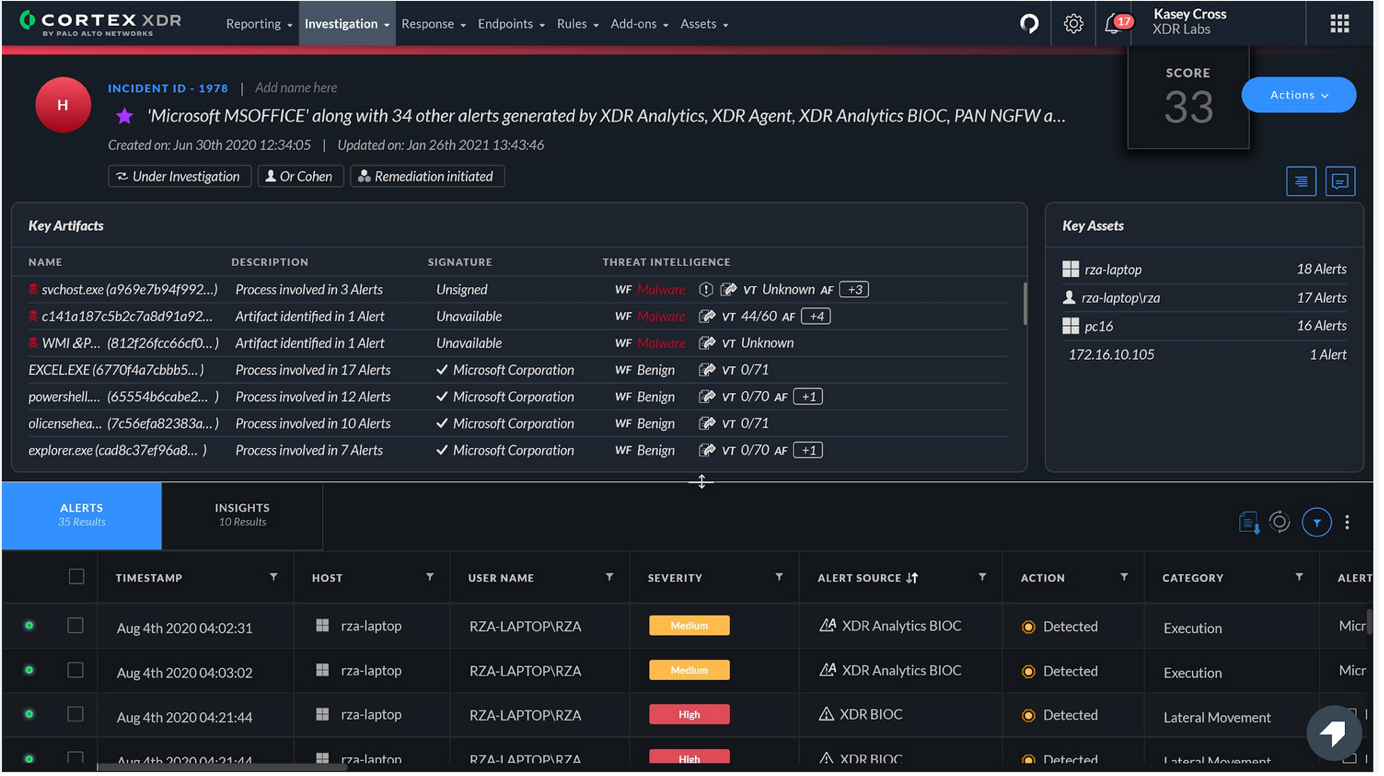
Security incident details, investigation context, and response workflows.
Our Implementation Approach
Assess
Reviewed endpoint configurations, network topology, existing security tools, and potential vulnerabilities.
Plan
Mapped Cortex XDR capabilities to security objectives, integration requirements, and operational risks.
Deploy
Installed Cortex XDR agents across endpoints and configured monitoring for relevant cloud workloads.
Integrate
Connected SIEM, firewall, anti-malware, and threat intelligence systems to support coordinated detection.
Validate
Performed simulated attacks and performance testing to verify detection, response, and system stability.
Enable
Trained the security team, established response guidance, and provided ongoing support and maintenance.
Technical Challenges & Solutions
Integrating Advanced Security Without Disrupting Operations.
Existing Security Tool Integration
Challenge: The client needed Cortex XDR to work alongside existing firewall, anti-malware, and SIEM platforms. Solution: Integrated security event forwarding, configured firewall threat intelligence sharing, and ensured compatibility with existing anti-malware software.
Enterprise-Wide Endpoint Coverage
Challenge: A growing, distributed environment required consistent endpoint protection and scalable security management. Solution: Deployed Cortex XDR agents across the endpoint estate and centralized management and monitoring.
Threat Detection & Operational Performance
Challenge: The solution needed to detect sophisticated threats while minimizing impact on endpoint and network performance. Solution: Conducted simulated attack testing and performance monitoring to validate detection, response, and operational stability.
Monitoring, Optimization & Handover
Continuous Threat Visibility and Faster Security Response.
Centralized Threat Monitoring
Cortex XDR provided a unified dashboard for monitoring endpoint activity, security alerts, and detected incidents.
Automated Incident Response
Automated response capabilities supported faster threat containment and remediation.
Reporting & Threat Analytics
SIEM integration and platform reporting enabled improved security event analysis and operational visibility.
Training & Ongoing Support
The client's security team received guidance on endpoint management, alert investigation, response playbooks, reporting, and troubleshooting.
Results & Business Impact
Stronger Protection. Greater Visibility. Faster Response.
Advanced Threat Protection
Improved detection of sophisticated threats across enterprise endpoints and cloud environments.
Faster Incident Response
Automated response capabilities reduced the time required to contain and remediate threats.
Centralized Security Visibility
Unified monitoring and SIEM integration improved visibility into incidents and security events.
Scalable Security Operations
Established a flexible security platform capable of supporting a growing endpoint and cloud environment.
Business Impact Summary
The deployment strengthened the client's overall security posture by combining advanced endpoint detection, automated response, centralized visibility, and integration with existing security tools. The client gained a scalable security platform that supports more effective threat identification, faster incident handling, and ongoing protection as its infrastructure expands.
Tools & Technology Used
Palo Alto Networks Cortex XDR
Cortex XDR Endpoint Agents
SIEM Integration
Firewall Integration
Threat Intelligence Feeds
Anti-Malware Integration
Cloud Workload Monitoring
Machine Learning Analytics
Behavioral Threat Detection
Automated Incident Response
Security Reporting
Incident Response Playbooks
Palo Alto Networks Cortex XDR
Cortex XDR Endpoint Agents
SIEM Integration
Firewall Integration
Threat Intelligence Feeds
Anti-Malware Integration
Cloud Workload Monitoring
Machine Learning Analytics
Behavioral Threat Detection
Automated Incident Response
Security Reporting
Incident Response Playbooks
Conclusion
Building a More Intelligent and Resilient Security Environment.
The Cortex XDR Deployment and Integration project delivered a comprehensive endpoint security solution that strengthened threat detection, centralized monitoring, and incident response.
Through structured planning, platform deployment, security tool integration, testing, and knowledge transfer, UI Operations established a scalable cybersecurity foundation that supports the client’s current operations and future security needs.
RELATED CASE STUDIES
Explore More Case Studies
LET’S BUILD WHAT’S NEXT
Is Your Organization Ready for More Advanced Threat Protection?
From endpoint security deployment to SIEM integration and automated incident response, UI Operations helps organizations build stronger, more resilient cybersecurity operations.