Case Study 09 — GCP Infrastructure & Direct Connectivity Integration
GCP Infrastructure Best Practices & Security Assessment
UI Operations assessed and optimized an enterprise Google Cloud environment, strengthening identity and access controls, improving cloud security, reducing infrastructure costs, and aligning operations with Google Cloud architecture best practices.
Google Cloud
Security Assessment
Compliance
Cloud Optimization
Project at a Glance
Client
Confidential Enterprise Client
Project
GCP Infrastructure Best Practices & Security Assessment
Service
Cloud Architecture & Security Consulting
Platform
Google Cloud Platform (GCP)
Solution
Infrastructure Security Assessment & Optimization
Focus
Security, Compliance, Cost Efficiency, Performance & Scalability
Conducted a comprehensive assessment of the client’s existing Google Cloud infrastructure, reviewing IAM permissions, VPC security, data protection, monitoring, compliance controls, and resource utilization. Implemented targeted improvements to reduce security risks, optimize cloud spending, and establish a more secure, scalable, and operationally efficient cloud environment.
The Challenge
Identifying Security Gaps and Inefficiencies Across a Growing Cloud Environment.
The client needed greater confidence that its Google Cloud infrastructure met security, compliance, performance, and operational best practices.
The assessment identified opportunities to tighten excessive access permissions, secure cloud storage configurations, and reduce unnecessary costs associated with underutilized resources.
Security Exposure
Excessive IAM permissions and configuration weaknesses increased the risk of unauthorized access.
Compliance & Governance
Cloud security controls, encryption, logging, and access policies needed evaluation against relevant regulatory requirements.
Resource & Cost Inefficiency
Underutilized compute resources and inefficient storage configurations created opportunities for cost optimization.
The Solution
A Comprehensive Approach to Cloud Security, Governance, and Performance.
UI Operations evaluated the client’s existing GCP architecture against Google Cloud best practices and implemented improvements across identity management, networking, storage, monitoring, and resource optimization.
The engagement combined security assessments, risk remediation, compliance reviews, and operational enhancements to establish a more resilient cloud foundation.
Identity & Access Security
Reviewed IAM roles, enforced least-privilege access, strengthened authentication, and improved permission management.
Network & Data Protection
Assessed VPC segmentation, firewall rules, Cloud Storage permissions, encryption, and Cloud KMS configurations.
Monitoring & Threat Detection
Configured centralized Cloud Monitoring, Cloud Logging, audit logs, alerts, and automated security response capabilities.
Cost & Performance Optimization
Right-sized compute resources, optimized storage classes, and improved scaling and cost management practices.
Architecture & Technology
Inside the Google Cloud Security & Infrastructure Assessment.
The assessment covered identity and access management, VPC networking, cloud storage, encryption, compute resources, monitoring, and security governance.
Strengthening Identity & Access Management
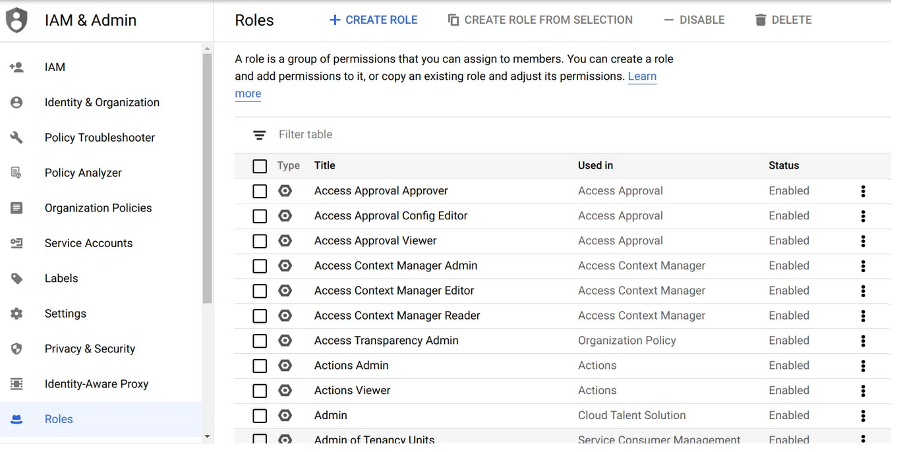
Google Cloud IAM role configurations reviewed to identify excessive permissions, enforce least-privilege access, and improve separation of duties.
Reviewing Cloud Network Security Architecture
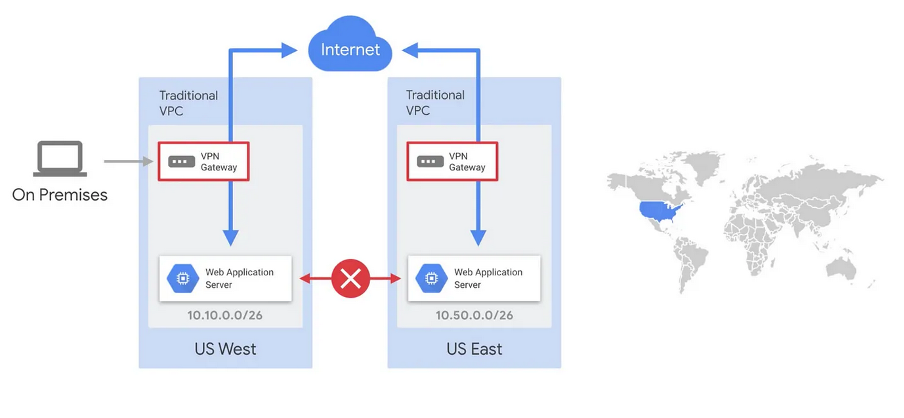
A reference network diagram illustrating regional VPC environments, VPN gateways, and protected application infrastructure.
Evaluating Cloud Resource Performance
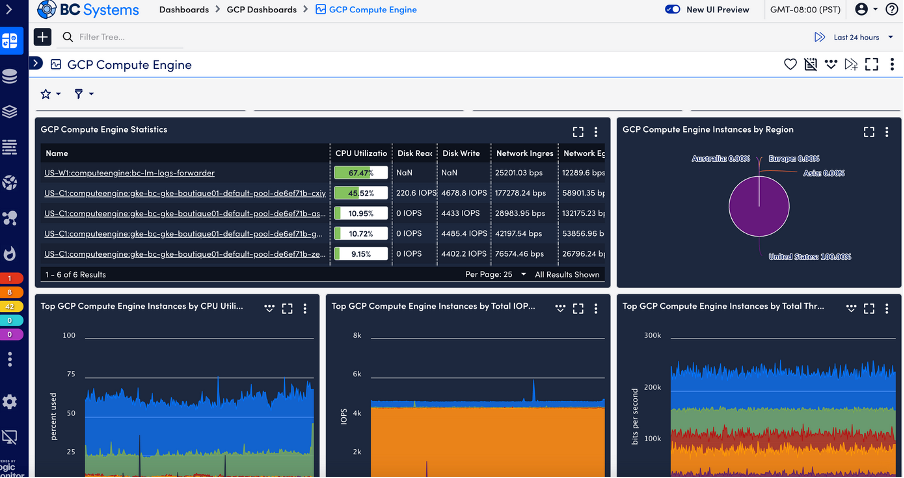
Compute Engine performance dashboards supporting visibility into resource utilization, operational health, and infrastructure optimization opportunities.
Our Implementation Approach
Discover
Reviewed existing GCP resources, stakeholder requirements, security priorities, and compliance obligations.
Assess
Evaluated IAM, VPC networks, Cloud Storage, encryption, security configurations, and infrastructure risks.
Align
Compared the environment against Google Cloud architecture best practices for security, performance, cost, and scalability.
Remediate
Strengthened permissions, restricted storage access, refined firewall rules, and improved security configurations.
Validate
Performed vulnerability assessments, targeted penetration testing, and compliance control reviews.
Optimize
Implemented monitoring, security automation, resource right-sizing, cost controls, and operational documentation.
Technical Challenges & Solutions
Resolving Security Risks and Cloud Infrastructure Inefficiencies.
Excessive IAM Permissions
Challenge: Overly broad access permissions increased the risk of unauthorized access to cloud resources. Solution: Audited IAM roles and permissions, enforced least-privilege access, and improved separation of duties.
Misconfigured Cloud Storage
Challenge: Cloud Storage bucket configurations required stronger access restrictions and data protection. Solution: Reviewed bucket permissions, restricted public access, strengthened encryption, and enabled versioning and logging on critical storage resources.
Cloud Cost Overruns
Challenge: Underutilized compute instances and inefficient storage allocation contributed to unnecessary cloud spending. Solution: Right-sized virtual machines, optimized storage classes, and identified opportunities for more cost-effective compute capacity.
Monitoring, Optimization & Handover
Continuous Monitoring and Smarter Cloud Operations.
Cloud Monitoring & Logging
Configured Cloud Monitoring, Cloud Logging, and audit logs to track infrastructure health, security events, and suspicious activity.
Automated Security Remediation
Used Cloud Functions and predefined policies to support automated security checks and responses to identified risks.
Cost Management & Resource Optimization
Established budgets and alerts, reviewed utilization, and optimized compute and storage configurations.
Documentation & Operational Guidance
Delivered security configuration records, best practices, and operational guidance to support ongoing cloud management.
Results & Business Impact
Stronger Security. Optimized Costs. Greater Cloud Resilience.
Improved Security Posture
Strengthened IAM permissions, encryption, network controls, and proactive security monitoring.
Reduced Cloud Costs
Improved resource utilization through compute right-sizing and more cost-effective storage configurations.
Improved Compliance Readiness
Enhanced audit logging, data protection, retention controls, and alignment with applicable regulatory requirements.
Scalable Cloud Operations
Improved infrastructure scalability, automated monitoring, and operational resilience to support future growth.
Business Impact Summary
The assessment and remediation project improved the client's Google Cloud security posture, reduced unnecessary infrastructure spending, strengthened compliance controls, and enhanced operational efficiency. The resulting environment provides a more secure and scalable foundation for ongoing cloud operations.
Tools & Technology Used
Google Cloud Compute Engine
Google Cloud VPC
Cloud Storage
Cloud IAM & Identity
Cloud KMS
Cloud Functions
Cloud Monitoring
Cloud Logging
Security Command Center
Google Cloud Armor
Identity-Aware Proxy
Google Kubernetes Engine
Cloud Audit Logs
Google Cloud Billing
Cloud Security Scanner
Google Cloud Compute Engine
Google Cloud VPC
Cloud Storage
Cloud IAM & Identity
Cloud KMS
Cloud Functions
Cloud Monitoring
Cloud Logging
Security Command Center
Google Cloud Armor
Identity-Aware Proxy
Google Kubernetes Engine
Cloud Audit Logs
Google Cloud Billing
Cloud Security Scanner
Conclusion
Building a Secure, Efficient, and Future-Ready Google Cloud Environment.
The GCP Infrastructure Best Practices and Security Assessment project delivered meaningful improvements across cloud security, governance, cost efficiency, and operational performance.
Through comprehensive assessment, targeted remediation, resource optimization, and continuous monitoring, UI Operations helped establish a more resilient Google Cloud environment aligned with the client’s evolving business and infrastructure requirements.
RELATED CASE STUDIES
Explore More Case Studies
LET’S BUILD WHAT’S NEXT
How Secure and Optimized Is Your Cloud Infrastructure?
From cloud security assessments and compliance reviews to performance optimization and ongoing operations, UI Operations helps organizations build secure, efficient, and scalable cloud environments.