CASE STUDY 02 / CLOUD SECURITY & OPTIMIZATION
AWS Infrastructure Best Practices and Security Assessment
How UI Operations assessed, secured, and optimized an enterprise AWS environment through best-practice architecture reviews, targeted remediation, and continuous monitoring.
AWS Security
Compliance
Well- Architected
Project at a Glance
Client
Confidential enterprise client
Project
AWS Infrastructure Best Practices & Security Assessment
Service
Cloud Architecture & Operations / Security Consulting
Platform
Amazon Web Services
Engagement
AWS Security Assessment & Remediation
Focus
Security, Compliance, Performance, Cost Optimization
UI Operations was engaged to assess and strengthen the client’s existing AWS environment. The project focused on identifying security vulnerabilities, aligning infrastructure with AWS best practices, improving operational efficiency, and optimizing cloud resources for future growth.
Through a structured assessment and remediation process, we helped the client reduce operational risks, improve cloud security controls, and establish a more resilient and manageable AWS environment.
The Challenge
Cloud Infrastructure Is Only as Strong as Its Security and Configuration.
As the client’s AWS environment evolved, maintaining consistent security, compliance, and operational efficiency became increasingly complex.
The organization needed greater visibility into its infrastructure, stronger access and data protection controls, and a practical approach to improving cloud performance without introducing unnecessary costs.
Security Exposure
Identify excessive IAM permissions, unsecured storage, encryption gaps, and network misconfigurations.
Compliance & Governance
Assess security controls against applicable regulatory requirements and AWS best practices.
Operational Efficiency
Improve resource utilization, monitoring, automation, and cost management.
The Solution
A More Secure, Efficient, and Resilient AWS Environment.
UI Operations conducted a comprehensive security and infrastructure assessment using AWS-native security, monitoring, and advisory tools.
The engagement combined configuration reviews, risk identification, targeted remediation, Well-Architected best-practice alignment, and operational improvements to strengthen the client’s AWS foundation.
Security Assessment
Reviewed IAM, VPC networking, S3 permissions, encryption, and infrastructure configurations.
Best Practices Alignment
Evaluated security, reliability, performance, operational excellence, and cost efficiency.
Risk Remediation
Addressed identified access, storage, encryption, and configuration weaknesses.
Monitoring & Optimization
Enhanced logging, alerting, incident response, resource management, and cost visibility.
Architecture & Technology
Inside the AWS Security Architecture.
The assessment covered the client’s AWS networking, access management, workload protection, logging, and security monitoring capabilities.
The architecture review included VPC configurations, security groups, NACLs, IAM permissions, S3 access controls, and data protection across relevant AWS resources.
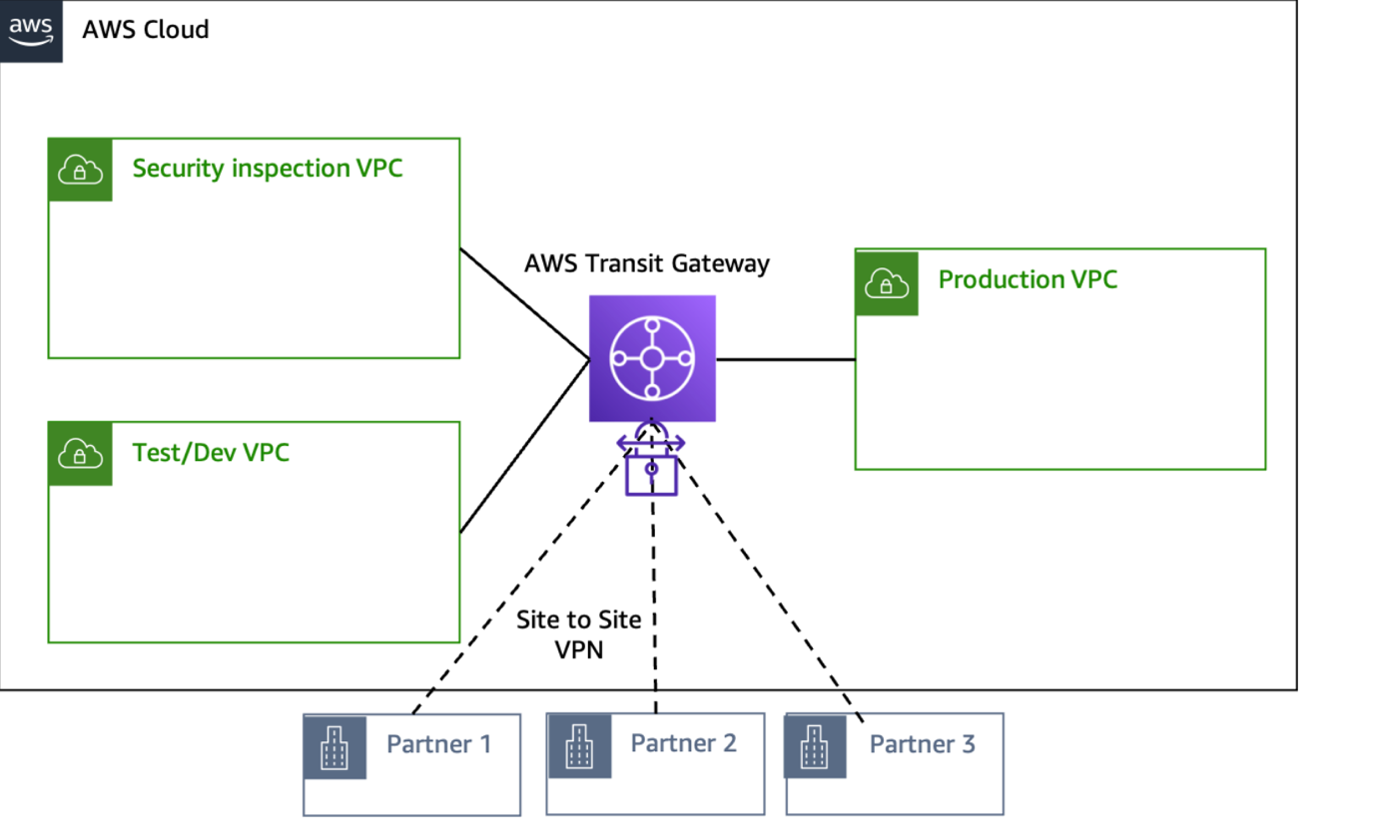
AWS Network Security
Illustrate the security inspection VPC, production and development environments, AWS Transit Gateway, and external connectivity.
AWS Infrastructure Review
Review of VPC, IAM, EC2, S3, and networking configurations.
Connectivity & Resilience Review
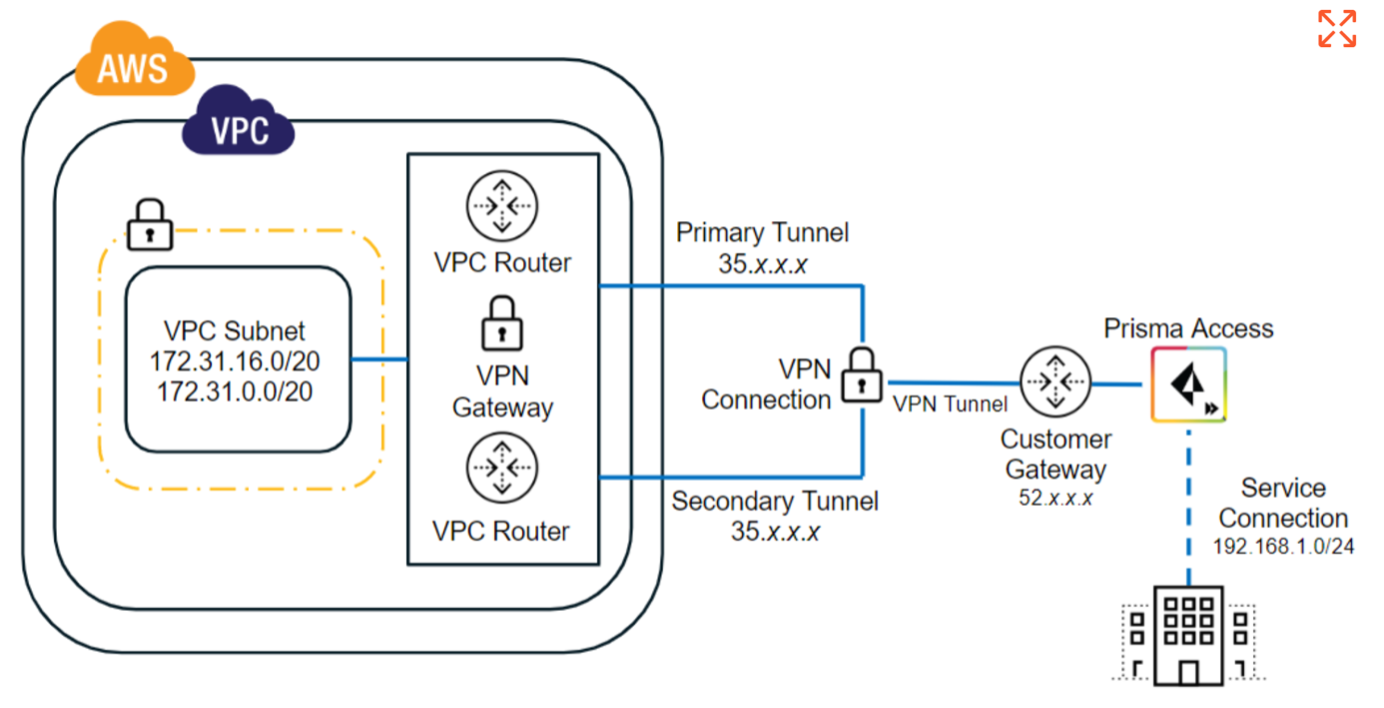
Assessment of network connectivity, secure access paths, and failover considerations.
Our Implementation Approach
Discover
Reviewed the AWS environment and gathered security, operational, and compliance requirements.
Assess
Evaluated IAM, VPC, S3, encryption, monitoring, and infrastructure security controls.
Align
Compared the environment against AWS Well-Architected best practices and relevant compliance requirements.
Remediate
Corrected identified vulnerabilities, improved access controls, and strengthened data protection.
Validate
Performed scoped security testing, recovery checks, and compliance verification.
Optimize
Enhanced monitoring, automation, resource utilization, cost visibility, and documentation.
Technical Challenges & Solutions
Addressing Critical Cloud Security Gaps.
Excessive IAM Permissions
Challenge: Overly permissive IAM roles and policies increased the risk of unauthorized access. Our Solution: Implemented role-based access controls and refined IAM permissions according to least-privilege principles.
Unsecured S3 Storage
Challenge: Storage configurations required stronger access restrictions and visibility. Our Solution: Audited S3 buckets, tightened access policies, and enabled logging and versioning to improve protection.
Data Encryption Gaps
Challenge: Sensitive data required consistent protection both at rest and in transit. Our Solution: Strengthened encryption configurations using AWS KMS and SSL/TLS where appropriate.
Monitoring, Optimization & Handover
Security and Operational Visibility Beyond the Assessment.
The engagement extended beyond identifying vulnerabilities. UI Operations introduced monitoring, automation, and optimization improvements to support the client’s ongoing AWS operations.
Continuous Security Monitoring
Configured CloudWatch, CloudTrail, and AWS Config to support event monitoring, configuration visibility, and security alerts.
Automation & Incident Response
Applied AWS Lambda and security services such as GuardDuty to support automated responses where appropriate.
Cost & Resource Optimization
Used Cost Explorer and Trusted Advisor insights to identify right-sizing opportunities, unused resources, and more efficient purchasing and storage options.
Documentation & Improvement Roadmap
Delivered security configuration documentation, operational guidance, and recommendations for continuous improvement.
Results & Business Impact
A Stronger Security Posture. A Smarter Cloud Environment.
Stronger Cloud Security
Improved IAM controls, storage security, encryption, and network protection.
Enhanced Compliance Readiness
Strengthened security controls, audit documentation, and alignment with applicable compliance requirements.
Improved Cost Efficiency
Reduced unnecessary resource expenditure through right-sizing, storage optimization, and purchasing recommendations.
Greater Operational Resilience
Improved monitoring, automation, scalability, and recovery readiness.
Business impact summary
The assessment and remediation engagement helped the client reduce security risks, improve resource efficiency, strengthen compliance readiness, and establish more reliable cloud operations.
Tools & Technology Used
AWS IAM
Amazon VPC
Amazon EC2
Amazon S3
AWS CloudTrail
Amazon CloudWatch
AWS Config
AWS Security Hub
Amazon GuardDuty
AWS Lambda
AWS Lambda
AWS IAM
Amazon VPC
Amazon EC2
Amazon S3
AWS CloudTrail
Amazon CloudWatch
AWS Config
AWS Security Hub
Amazon GuardDuty
AWS Lambda
AWS Lambda
Conclusion
A Stronger Security Posture. A Smarter Cloud Environment.
The AWS Infrastructure Best Practices and Security Assessment project helped the client strengthen its AWS security posture, improve infrastructure efficiency, and establish more consistent operational controls.
Through security remediation, best-practice alignment, continuous monitoring, and resource optimization, UI Operations delivered a stronger foundation for secure, scalable, and resilient cloud operations.
RELATED CASE STUDIES
Explore More Case Studies
LET’S BUILD WHAT’S NEXT
Is Your AWS Infrastructure Secure, Efficient, and Ready to Scale?
From cloud security assessments to architecture optimization and operational improvements, UI Operations helps businesses build more secure, reliable, and efficient AWS environments.